Ledger confirms spy chip implant behind wallet crypto thefts
Ledger confirms spy chip implant behind wallet crypto thefts
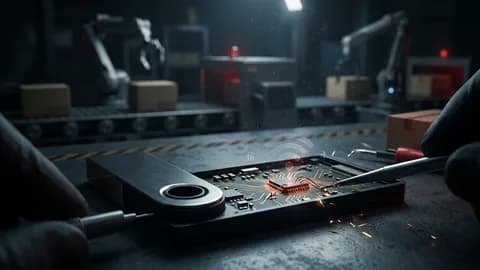
Ledger has confirmed that some of its hardware wallets distributed through Southeast Asian reseller CryptoBilis were physically tampered with and fitted with a spy chip that drained users' cryptocurrency. The discovery follows multiple reports of unexpected wallet losses and forensic analysis showing a small LTE-capable implant inside compromised Ledger X devices.
Supply chain compromise via an unauthorized reseller
Ledger wallets are designed to keep private keys offline, but the security model assumes the device itself hasn't been physically modified before reaching the end user. In this incident, the attack vector wasn't a software vulnerability in Ledger's firmware or apps — it was hardware tampering in the supply chain, with devices sold through an unauthorized channel.
On October 9, Ledger launched an investigation after users reported unauthorized withdrawals. The next day it confirmed hardware tampering on at least one affected device and urged anyone who purchased a Ledger device from CryptoBilis to not set it up, or if already set up, to move funds to a new signer with a new recovery phrase. By October 11, Ledger stated that all reported unexpected drains traced back to CryptoBilis and described the affected set as limited.
While Ledger didn't name specific models in its public statements, independent researchers have focused on Ledger Nano X devices that were purchased through third-party sellers shipping from Malaysia. The common thread is that these devices were not acquired through Ledger's authorized sales channels.
What the implant does and how it works
Forensic teardown of tampered Ledger Nano X units shows a covert hardware implant designed to capture the user's recovery phrase as it's entered on the device. The implant sits inside the case and uses a small antenna to exfiltrate data over an LTE cellular connection, meaning it can transmit the stolen seed phrase without requiring the compromised wallet to connect to Wi-Fi or a paired phone in a suspicious way.
Two distinct variants have been documented. One places the implant under the battery with a shielded LTE module and a tiny eSIM; the other, more compact, fits in the space normally occupied by foam padding under the OLED display and runs off the original battery while hiding an antenna along the top edge of the case. In both cases, the telltale sign is a thin antenna wire that doesn't belong to the original hardware. Some modules also had part numbers scraped off in an attempt to obscure their identity.
Once powered on, the implant records the display output and button presses during device setup or recovery. That allows it to capture the 24-word recovery phrase as the user enters or verifies it. With the seed phrase in hand, the attacker can reconstruct the private keys and drain funds from the wallet at a later time — often without any obvious signs on the device's interface during the theft window.
Indicators to watch for
A key lesson from this case is that "genuine" firmware checks alone aren't enough to detect a physical implant if the Secure Element remains intact. Ledger's Genuine Check verifies authenticity in some dimensions, but it explicitly doesn't guarantee the absence of added hardware modifications.
Practical red flags that could suggest tampering include: a different battery fit, visible or loose antenna wiring, unexpected thickness/packing differences, or a device that was purchased well below retail from an unknown third-party seller shipping from a suspicious source. None of these are definitive on their own, but combined with an unauthorized purchase channel they should raise concern.
If you bought a Ledger device from CryptoBilis and haven't set it up, do not initialize it. If you've already set it up, treat the recovery phrase as potentially compromised — create a new wallet (new seed) on a known-good device from an authorized channel and move your assets there.
Takeaway
This incident is a reminder that hardware wallets protect against remote malware, but they don't eliminate supply chain risk. The strongest defense is simple: buy hardware wallets only from the manufacturer's authorized resellers or directly from the official store, verify packaging on arrival, and if in doubt, don't use a device whose physical integrity can't be confirmed.
Sources
- BleepingComputer: Ledger confirms spy chip implant behind wallet crypto thefts
- CoinDesk: Ledger says unauthorized implant found in at least one device sold by CryptoBilis
- Help Net Security: Hidden implant in Ledger hardware wallets linked to $93M theft
- ETHNews: Ledger Buyers Lost Millions as Spy Chip Found Inside a Wallet
// author
Editor & Operator
Mohd Firdaus Abu Bakar (MrDodgerX) is an enterprise geospatial systems engineer in Malaysia and the editor behind hejes.my. He runs the briefing pipeline, curates and edits every draft, verifies each factual claim against primary sources, and presses the publish button — nothing ships without his review. He writes about AI, security and Malaysia's tech scene from a builder's perspective. Professional profile and code: the links below.
// sources //
fact-check verified · 13 OCT 2026 · hejes-content-fact-check
- Ledger confirms spy chip implant behind wallet crypto theftsBleepingComputer · accessed 13 OCT 2026
- Ledger says unauthorized implant found in at least one device sold by CryptoBilisCoinDesk · accessed 13 OCT 2026
- Hidden implant in Ledger hardware wallets linked to $93M theftHelp Net Security · accessed 13 OCT 2026
- Ledger Buyers Lost Millions as Spy Chip Found Inside a WalletETHNews · accessed 13 OCT 2026
related //
15,465 MCP Servers and Almost No Governance
OX Security mapped 15,465 public MCP servers: 15.6% hosted outside the US, 2.3% of domains already dead. The protocol is fine. The trust isn't.
Placeholder domains now serve malware. Audit your docs.
third-party.com, the docs placeholder everyone copied, now serves ClickFix; 13 lookalike domains carry scams. Static checks miss all of it — audit your docs.
GitLab Issue Email Is a Push-to-Main Token
GitLab's "Email work item" address hides an account-wide token. Leak it and anyone can push to main, run CI jobs as you, and skip IP allowlists.
// join the feed
one fresh insight per week. no spam, ever.
weekly digest. unsubscribe anytime.